Deploy AWS Cognito Cross Sites
Introduction to Cognito
Amazon Cognito is an identity authentication platform for web and mobile applications. It includes a user directory, an authentication server, and an authorization service for OAuth 2.0 access tokens and AWS credentials. With Amazon Cognito, you can authenticate and authorize users from the built-in user directory, from your enterprise directory, and from consumer identity providers.
The following two components make up Amazon Cognito. They operate independently or together, depending on the access needs of your users.

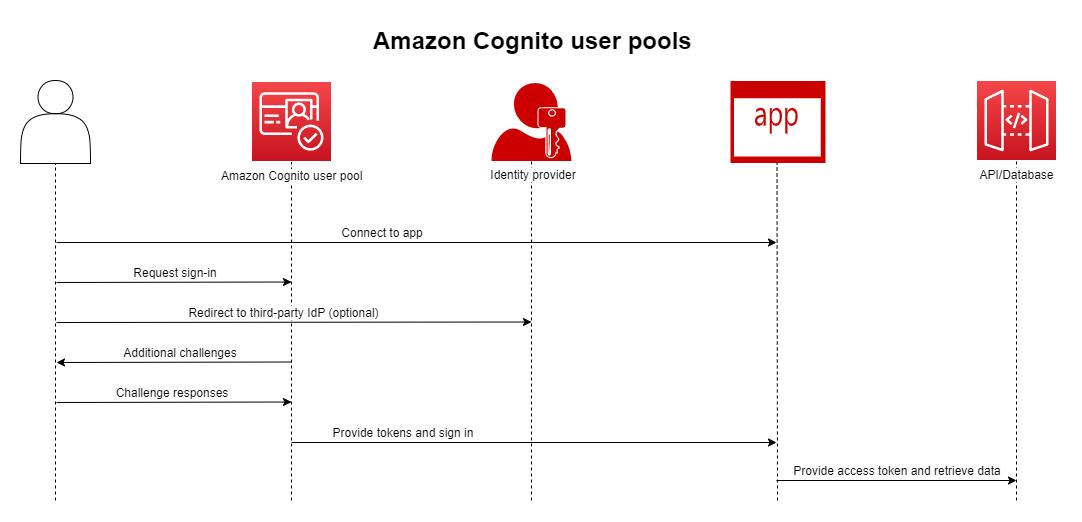
User Pool
Create a user pool when you want to authenticate and authorize users for your application or API. User pools are a user directory with both self-service and administrator-driven user creation and management features. Your user pool can be an independent directory and an OIDC identity provider (IdP), as well as a service provider (SP) intermediary for third-party providers of workforce and customer identities. Your organization’s SAML 2.0 and OIDC IdPs bring workforce identities into Cognito and your application. Public OAuth 2.0 identity repositories like Amazon, Google, Apple, and Facebook bring customer identities in.
User pools do not require integration with an identity pool. From a user pool, you can directly issue authenticated JSON web tokens (JWTs) to an application, web server, or API.
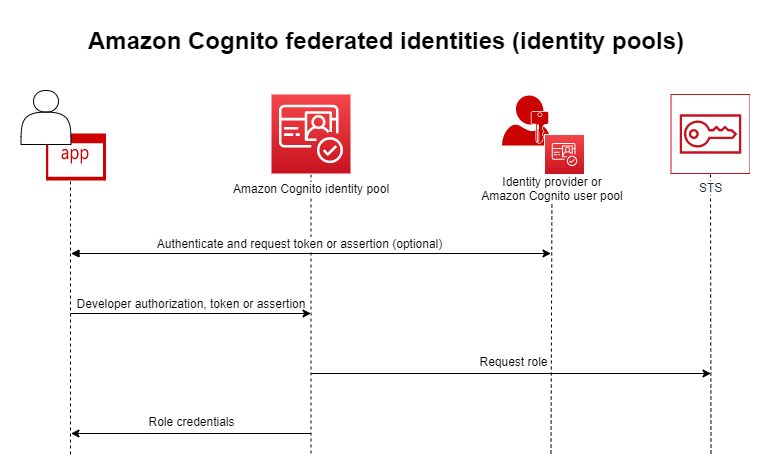
Identity pools
Set up an Amazon Cognito identity pool when you want to grant access to AWS resources to authenticated or anonymous users. An identity pool grants AWS credentials to your application to serve resources to users. You can authenticate users with a trusted identity provider, such as a user pool or a SAML 2.0 service. It can also optionally grant credentials to guest users. The identity pool uses both role-based and attribute-based access control to manage user access to your AWS resources.